Companies and public-sector organisations are now fully dependent on their supply chain for almost all their activities. This is because it is impossible to operate efficiently without relying on tools and experts to run every department within an organisation: IT, HR, logistics,…
ARTICLE
Cyber Provider Risk: A Major Strategic Challenge
The digital supply chain has become the weak link for many organizations. Recent attacks—such as those targeting Jaguar Land Rover, Marks & Spencer, or compromises via Managed Service Providers (MSPs)—have demonstrated that a vulne…
ARTICLE
The due diligence process, also known as reasonable diligence, is an essential in-depth investigation that companies must perform before establishing business relationships with third parties, particularly suppliers. This process often includes a supplier due diligence to assess …
ARTICLE
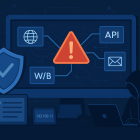
External Attack Surface Management (EASM): assess, prioritize, remediate
External Attack Surface Management (EASM) encompasses the practices, procedures, and tools aimed at mapping, monitoring, and securing all of a company’s digital assets exposed on the Internet. It provides or…
ARTICLE
When a company applies for or renews cyber insurance, the insurer does not simply check whether it has antivirus software or a security policy in place. It seeks to answer a more practical question: what is the organisation's actual level of exposure, and how well can it limit th…
ARTICLE
In a digital landscape where corporate boundaries are dissolving into interconnected ecosystems, your organization's security no longer depends solely on your own ramparts, but on the strength of every link in your supply chain. Third-Party Risk Management (TPRM) has shifted from…
ARTICLE