Kit de Rentrée des DSI & RSSI – Édition 2026

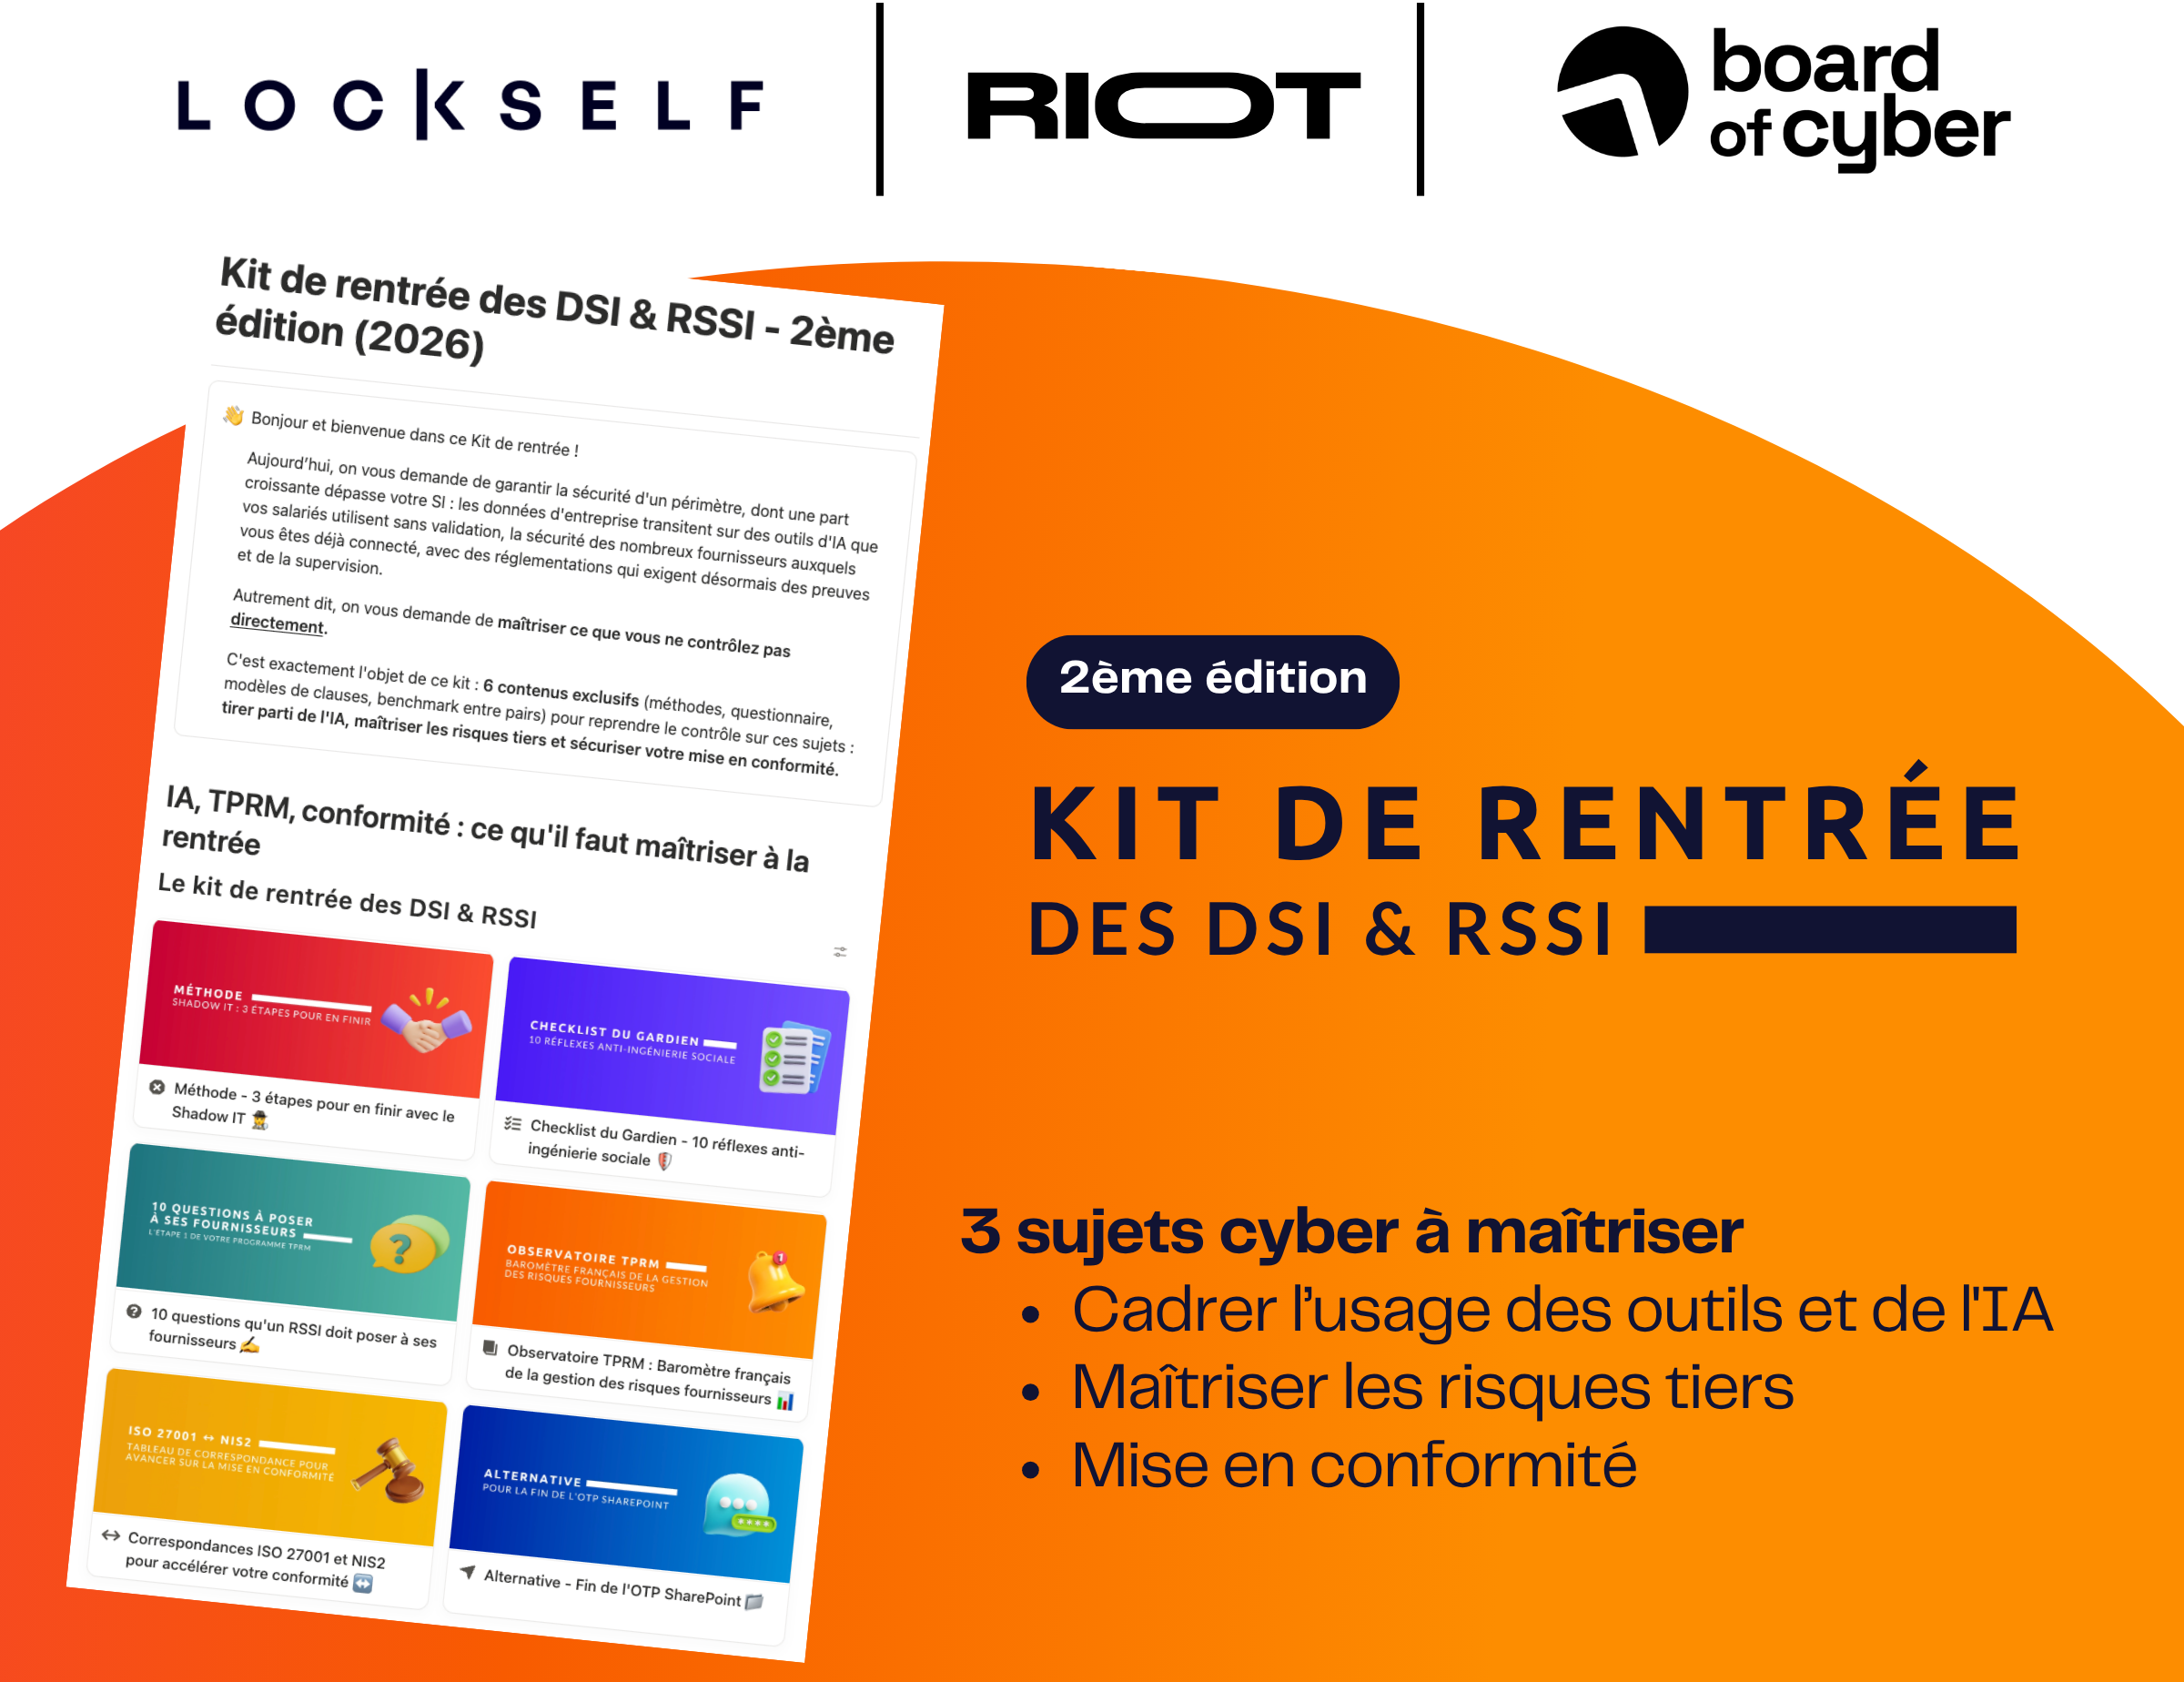
Facilitez votre rentrée avec 6 outils concrets pour sécuriser votre périmètre, maîtriser vos risques tiers et avancer sur la conformité. Un guide pratique par LockSelf, Riot et Board of Cyber.

Pourquoi ce kit est essentiel cette rentrée ?

Le périmètre de sécurité ne s’arrête plus à vos serveurs. Vos données transitent via des outils d’IA non validés, vos fournisseurs représentent un vecteur de risque majeur, et les réglementations (NIS2, DORA) exigent désormais de la preuve et de la supervision continue. Ce kit a été conçu pour vous donner les leviers concrets pour reprendre le contrôle sur ce que vous ne gérez pas directement.

CISO, CIO, PROCUREMENT DEPARTMENT, INSURERS… THEY HAVE BUILT THEIR ECOSYSTEM OF TRUST

“A poorly secured Active Directory is a prime target for cybercriminals. By continuously assessing Active Directory security, we have structured our approach with great precision.”

Samuel BAFOURD

CIO of the Seven2 investment fund

Discover the testimonial

“We have a perfect understanding of our external exposure surface across all the firms in the group. Thanks to the experts' platform, we are able to communicate on our maturity.”

Frédéric SOULIER

Deputy CIO and CISO, CMS Francis Lefebvre Lawyers

Discover the testimonial
  • Méthode : 3 étapes pour en finir avec le Shadow IT
    Une approche structurée pour identifier, contrôler et sécuriser les applications utilisées sans validation par vos équipes.


  • Checklist du Gardien : 10 réflexes anti-ingénierie sociale
    Les bonnes pratiques essentielles pour renforcer la résilience de vos collaborateurs face aux attaques ciblées.


  • 10 questions qu’un RSSI doit poser à ses fournisseurs
    Le questionnaire clé pour évaluer rapidement la maturité cyber de vos prestataires critiques. L’étape 1 de votre programme TPRM.
  • Observatoire TPRM : Baromètre français de la gestion des risques fournisseurs
    Comparez vos pratiques avec celles de vos pairs grâce à notre étude exclusive sur l’état de la Third-Party Risk Management en France.


  • Tableau de correspondance ISO 27001 ↔ NIS2
    Accélérez votre mise en conformité en identifiant précisément ce que votre certification ISO couvre déjà au regard des exigences NIS2.


  • Alternative : Fin de l’OTP SharePoint
    Découvrez les solutions modernes pour remplacer les mécanismes obsolètes et sécuriser davantage le partage de documents.

WEBINAIRE : PASSEZ DE LA THÉORIE À LA PRATIQUE

IA générative, risques fournisseurs, conformité : découvrez des pistes d'action concrètes pour renforcer votre maîtrise des risques cyber.

📆 Mardi 27 octobre 2026 - 11h00
Format en ligne - 45 minutes + questions/réponses

Riot, LockSelf et Board of Cyber réunissent leurs expertises pour vous aider à sensibiliser vos collaborateurs, sécuriser vos données sensibles et piloter les risques de votre organisation et de son écosystème.

  • Développer les bons réflexes cyber face aux menaces du quotidien
  • Sécuriser les mots de passe, les partages documentaires et les données sensibles
  • Évaluer et piloter en continu le niveau de risque cyber

Large corporations, SMEs, the public sector: cybersecurity does not affect everyone in the same way

Large enterprises: manage your cyber risk at scale

As the organisation grows, the attack surface expands: subsidiaries, subcontractors, cloud environments, Active Directory… The sheer number of different areas makes it impossible to manage the system as a whole without consolidation.
  • A unified view of the cyber performance of the organisation and its entities
  • Ongoing monitoring of third parties and critical suppliers
  • Executive dashboards for the Executive Committee and the Board of Directors
  • NIS2 / DORA compliance with integrated audit trail

SMEs and mid-market companies: cybersecurity without a dedicated team

SMEs and mid-market companies are prime targets for attackers — and the first to lack the resources to defend themselves. Without a full-time CISO, they need tools that provide clear, actionable insights, without unnecessary complexity.
  • Instant cyber score, with no complex technical setup required
  • Identification of priority vulnerabilities requiring rectification and practical recommendations
  • A security policy that can be shared with your clients, partners or insurers

Banks and Insurance: meet DORA requirements without overburdening your teams

The financial sector is subject to the strictest requirements in terms of cyber resilience. In particular, DORA mandates rigorous oversight of critical IT service providers, a requirement that is difficult to meet without automation.
  • Ongoing assessment of your IT service providers’ performance
  • Centralisation of supplier questionnaires, audit evidence and the monitoring of corrective action plans
  • Your organisation’s consolidated cyber score, which can be shared with your risk and compliance teams
  • Ready-to-use executive dashboards for your internal and regulatory reporting

Local authorities and public services: secure your essential services in line with NIS2 requirements

Local authorities and public bodies now fall within the scope of NIS2 — often with limited resources and growing exposure to cyberattacks. The challenge is to establish a credible security framework without deploying disproportionate resources.
  • Assessment of cyber maturity level, in accordance with NIS2 requirements
  • Management of risks associated with service providers and software vendors
  • Ready-to-use reporting for regulatory authorities and ANSSI
  • Gradual support without the need for dedicated in-house expertise

Private Equity Funds: Assess the cyber risk in your portfolio

A cyber incident involving an investment can devalue a target, prevent a deal from closing, or result in the fund being held liable. However, cyber risk is rarely assessed during due diligence due to a lack of suitable, independent tools.
  • Cyber risk assessment of a target prior to closing, without access to its internal network
  • Consolidated monitoring of the cyber security posture across the entire portfolio
  • Identifying the most exposed investments in order to prioritise post-acquisition actions
  • Exportable report for investment committees