TrustCycle:

Manage your supplier cyber risks based on evidence, not just self-declarations

Repeated questionnaires, follow-ups, manual analyses: your teams cannot assess everything.
TrustCycle is the first platform to centralise both your client and supplier roles: assess your third parties and share your own cyber maturity with your clients. AI-powered analysis of documentary evidence and external cyber ratings save you time, allowing you to extend your assessments across your entire ecosystem. Translated with DeepL.com (free version)

TOO MANY SUPPLIERS. TOO MANY REQUESTS. NOT ENOUGH TRANSPARENCY

Your portfolio exceeds your ability to assess it

You assess the most critical suppliers. The others remain off your radar due to a lack of time and resources.

Data collection takes precedence over risk analysis

Questionnaires, follow-ups, scattered documents: your teams spend too much time gathering information and not enough time addressing discrepancies.

Your assessments become snapshots of the past

Services evolve and documents change. A one-off assessment is not enough to monitor your suppliers’ cyber maturity.

To assess more suppliers, we need to change our approach. We shouldn’t just keep sending out more questionnaires.

Assess more extensively, analyse more quickly, pool your efforts

Two analyses offering a complementary perspective

TrustCycle uses AI to analyse your suppliers’ security documentation and supporting evidence. Security Rating complements this assessment by analysing their external exposure.

All your suppliers, without the need for new questionnaires

Automate the analysis of existing security documents to reduce manual work. Extend your coverage beyond critical third parties and focus your teams on the gaps that need addressing.

A platform for both your roles

Assess your third parties as a client and share your maturity as a supplier. Centralise your documentation and reuse it with multiple authorised clients.

An assessment tailored to each client

The same service can be assessed according to each client’s requirements, thanks to customisable security profiles. The results are supported by documentary evidence.

Description de l’image

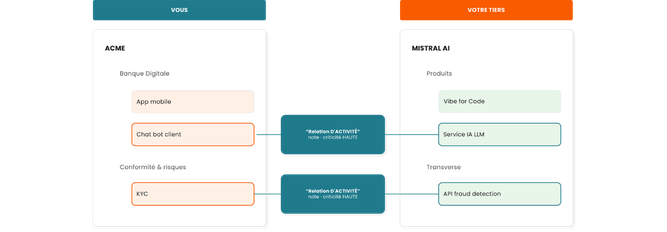
One platform for your customer and supplier profiles

In an ecosystem, everyone is both a customer and a supplier. With TrustCycle, manage both roles in one place: assess your third parties and share your own cybersecurity maturity with your authorised customers.

Your organisation in TrustCycle
As a customer

Assess and monitor your suppliers

Access your assessments in a consolidated view and interpret them in the context of the service used and your security requirements.

As a supplier

Centralise your supporting documentation

Upload and update your security documentation in one place. Reuse this documentation for assessments by multiple authorised customers, without collecting it all again.

Your relationships, security documentation and assessments are centralised on a single platform

You stay in control of access
As a supplier, you authorise the relationships that allow your customers to view your assessment.

Identify where to take action within your supplier portfolio

Switch from a consolidated view of your suppliers to a detailed view of a specific service or control to identify priorities, understand variances and guide your actions.
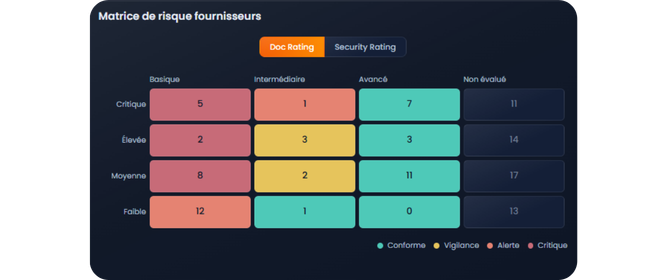
Focus your efforts on priority relationships

Cross-reference your suppliers’ criticality against their assessed maturity to identify relationships that require further investigation or closer monitoring.

Switch from the group view to the service in use

View your ratings at group, business unit or activity level. Filter services from the same provider to examine the scope that applies to you.
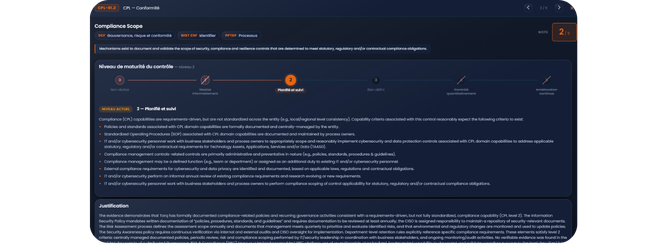
Trace the result back to the elements that justify it

Explore the results by category and by assessment. Find the reference materials that support the level awarded and the criteria required to reach the next level.

Your safety documents are turned into assessments

Import your suppliers

Link the services they provide to your operations and define the security profiles that meet your requirements.

Gather the existing documents

Your suppliers submit their safety documentation: policies, procedures, safety assurance plans and completed questionnaires.

AI analyses documentary evidence

For each assessment against the SCF framework, the AI identifies the documented evidence required to assign a maturity level and cites the sources used.

Update the documents, restart the assessment

When a supplier adds or updates their documentation, the analysis is restarted. The assessment is updated as new information becomes available.

A COMMON FRAMEWORK FOR DOCUMENTING YOUR CYBER SECURITY REQUIREMENTS

Use a structured reference framework

TrustCycle bases its document analysis on the Secure Controls Framework (SCF), using a common maturity scale to assess your suppliers.

Tailor the profiles to your requirements

Use the standard NIS2 and DORA profiles, then adjust the weighting of the controls according to your context and the services concerned.

Support your reviews and prepare for your audits

Compile the assessments and the supporting documentation to underpin your discussions with the Cyber, Procurement and Compliance teams.

FAQ
What is a supplier cyber risk management platform?
A supplier cyber risk management platform helps an organisation to centralise information on its third parties, assess their security maturity and monitor the risks associated with the services used. TrustCycle combines AI-powered document analysis, external ratings and context-specific analysis by business activity to support this process.
How can you assess a supplier’s cybersecurity without a questionnaire?
TrustCycle analyses the supplier’s existing security documentation in the SCF repository and supplements it with an assessment of their external exposure. This process reduces the need for questionnaires. However, depending on the criticality of the service and the information available, targeted checks or additional audits may still be necessary.
What is the difference between TrustCycle and an external cyber rating solution?
An external rating solution assesses security indicators observable via the internet. TrustCycle adds AI-powered document analysis and modelling of customer-supplier activities. This provides you with a complementary assessment of maturity, contextualised according to the service used.
Can the same supplier have different ratings depending on the service?
Yes. TrustCycle links your activities to those of your suppliers. The assessment takes into account the service actually used and the weighting of the controls applicable to your specific context.
Can you be both a customer and a supplier on TrustCycle?
Yes. The platform is based on this dual approach: you can assess your suppliers whilst demonstrating your own cyber maturity to your clients.
What is the difference between TrustCycle and Trust HQ®?
TrustCycle focuses on the automated, contextualised and collaborative assessment of third parties’ cyber maturity. Trust HQ® provides a broader scope for managing cyber governance: security policies, multi-standard compliance, audit campaigns using questionnaires, and the monitoring of action plans.
Does TrustCycle replace a security audit?
No. Document review and external assessment provide additional information, but do not, on their own, verify the effectiveness of all security controls. The depth of the checks must remain proportionate to the criticality of the service, the results obtained and the applicable obligations.